Attackers hijacked Danfoss refrigeration controls in a single day and pushed circumstances to 122F. The US is the Danish provider’s greatest single market
Hackers turned refrigerated circumstances at a whole bunch of French supermarkets into one thing nearer to ovens in a single day Sunday. They drove temperatures as excessive as 50C (122F), spoiled contemporary and frozen inventory and, in accordance with Paris prosecutors, sparked fires.
The assault ran by way of the evening of Oct. 11–12 and hit refrigeration management techniques made by Danish engineering group Danfoss. The attackers didn’t minimize the cooling. As an alternative, they reportedly hijacked a routine upkeep setting and locked models right into a nonstop defrost cycle. Les Mousquetaires, proprietor of the Intermarché chain, mentioned affected circumstances ran scorching for about six hours.
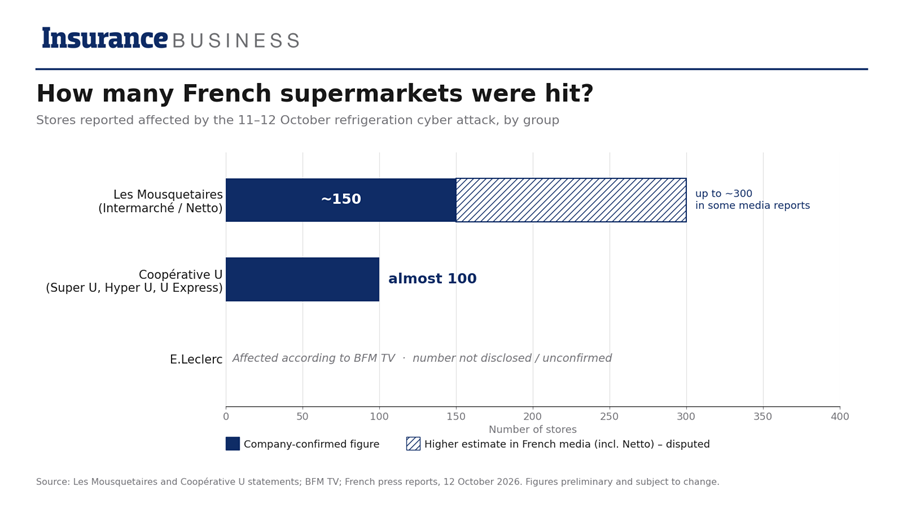
The group mentioned roughly 150 Intermarché shops had been hit and that every one contemporary and frozen product at these areas was thrown out. Some French media studies put the group’s whole nearer to 300 as soon as its Netto low cost shops are included. Coopérative U mentioned nearly 100 of its shops had been affected. Broadcaster BFM TV reported that E.Leclerc, France’s largest grocer, was additionally caught up.
Coopérative U CEO Dominique Schelcher posted on X that focusing on gear important to maintaining the nation’s meals contemporary was “unprecedented” and “unacceptable.”
French press studies say Les Mousquetaires places its losses within the hundreds of thousands of euros. Particular person retailer managers have described write-offs from about €50,000 to greater than €200,000 per location.
Paris prosecutors have opened an investigation into what they referred to as a “large-scale” assault. Prime Minister Sébastien Lecornu has requested France’s nationwide cybersecurity company, ANSSI, to analyze. His workplace mentioned France is coordinating with European companions as a result of different nations might also be uncovered.
Learn subsequent: We don’t know the place 40,000 new automobiles are – JLR
A identified flaw and a federal warning
A supply near Lecornu mentioned ANSSI had discovered a vulnerability in Danfoss software program. Danfoss mentioned it was conscious of incidents affecting “a restricted quantity” of French techniques operating outdated firmware. It added that it had lengthy urged clients to replace and retire legacy gear.
US operators had been warned. In Might 2025, the Cybersecurity and Infrastructure Safety Company printed an advisory on an authentication flaw in Danfoss’s AK-SM 800A system managers, which run grocery store refrigeration. In August this 12 months, researchers at Claroty’s Team82 unit detailed additional flaws in the identical platform, which Danfoss has since patched. In addition they reported hundreds of the controllers reachable from the open web, and located comparable weaknesses in Copeland’s XWEB Professional controllers. Investigators haven’t mentioned whether or not any of these particular flaws had been utilized in France.
That ought to concern operators within the US. Danfoss runs its North American enterprise from Baltimore, and the US has been described as its largest single-country market. To this point there’s no indication that any US retailer has been hit.
Who pays?
Intermarché has already warned that a few of its insurance policies might not cowl this type of in-store incident. US policyholders might run into the identical drawback.
Spoilage endorsements on business property insurance policies are sometimes written round energy outages or mechanical breakdown. However property carriers have spent years tightening cyber exclusions. Gallagher’s John Farley has informed Insurance coverage Enterprise that conventional property insurance policies usually carve out cyber-related bodily harm, whereas standalone cyber insurance policies differ extensively on whether or not they cowl property harm in any respect. A walk-in cooler stuffed with ruined meat might fall straight into that silent cyber hole.
Bodily harm brought on by a cyber assault could be insured, however usually solely when the enterprise buys that cowl intentionally. That may imply an endorsement on the cyber program or a devoted cyber-property product.
There’s a subrogation angle, too. Les Mousquetaires has reportedly mentioned the techniques had been managed by Danfoss. Any service that pays a declare might subsequently take a look at recovering its prices from additional up the chain.
Learn subsequent: Jaguar Land Rover failed to complete cyber insurance coverage buy
Grocery’s rising cyber invoice
US meals retail has been hit earlier than, although on the IT aspect. Final 12 months’s assault on distributor United Pure Meals minimize as much as $400 million from its gross sales and left Complete Meals cabinets naked, and the corporate mentioned it anticipated its cyber insurance coverage to cowl the incident.
Individually, Ahold Delhaize, the Dutch group that additionally owns Meals Lion, Cease & Store and Big, mentioned Monday it was coping with a “safety difficulty” affecting its shops within the Netherlands and Belgium. No hyperlink to the French assault has been established, and the reported disruption centered on its European chains.
The French assault was completely different. The attackers ignored the info and went straight for the bodily inventory.
Brokers with grocery, cold-storage and meals distribution shoppers might want two solutions this week. Is the refrigeration management gear related to the web, and is it patched? And which coverage pays if somebody units it to 122F?
Learn subsequent: What UK retail breaches imply for the worldwide cyber insurance coverage market